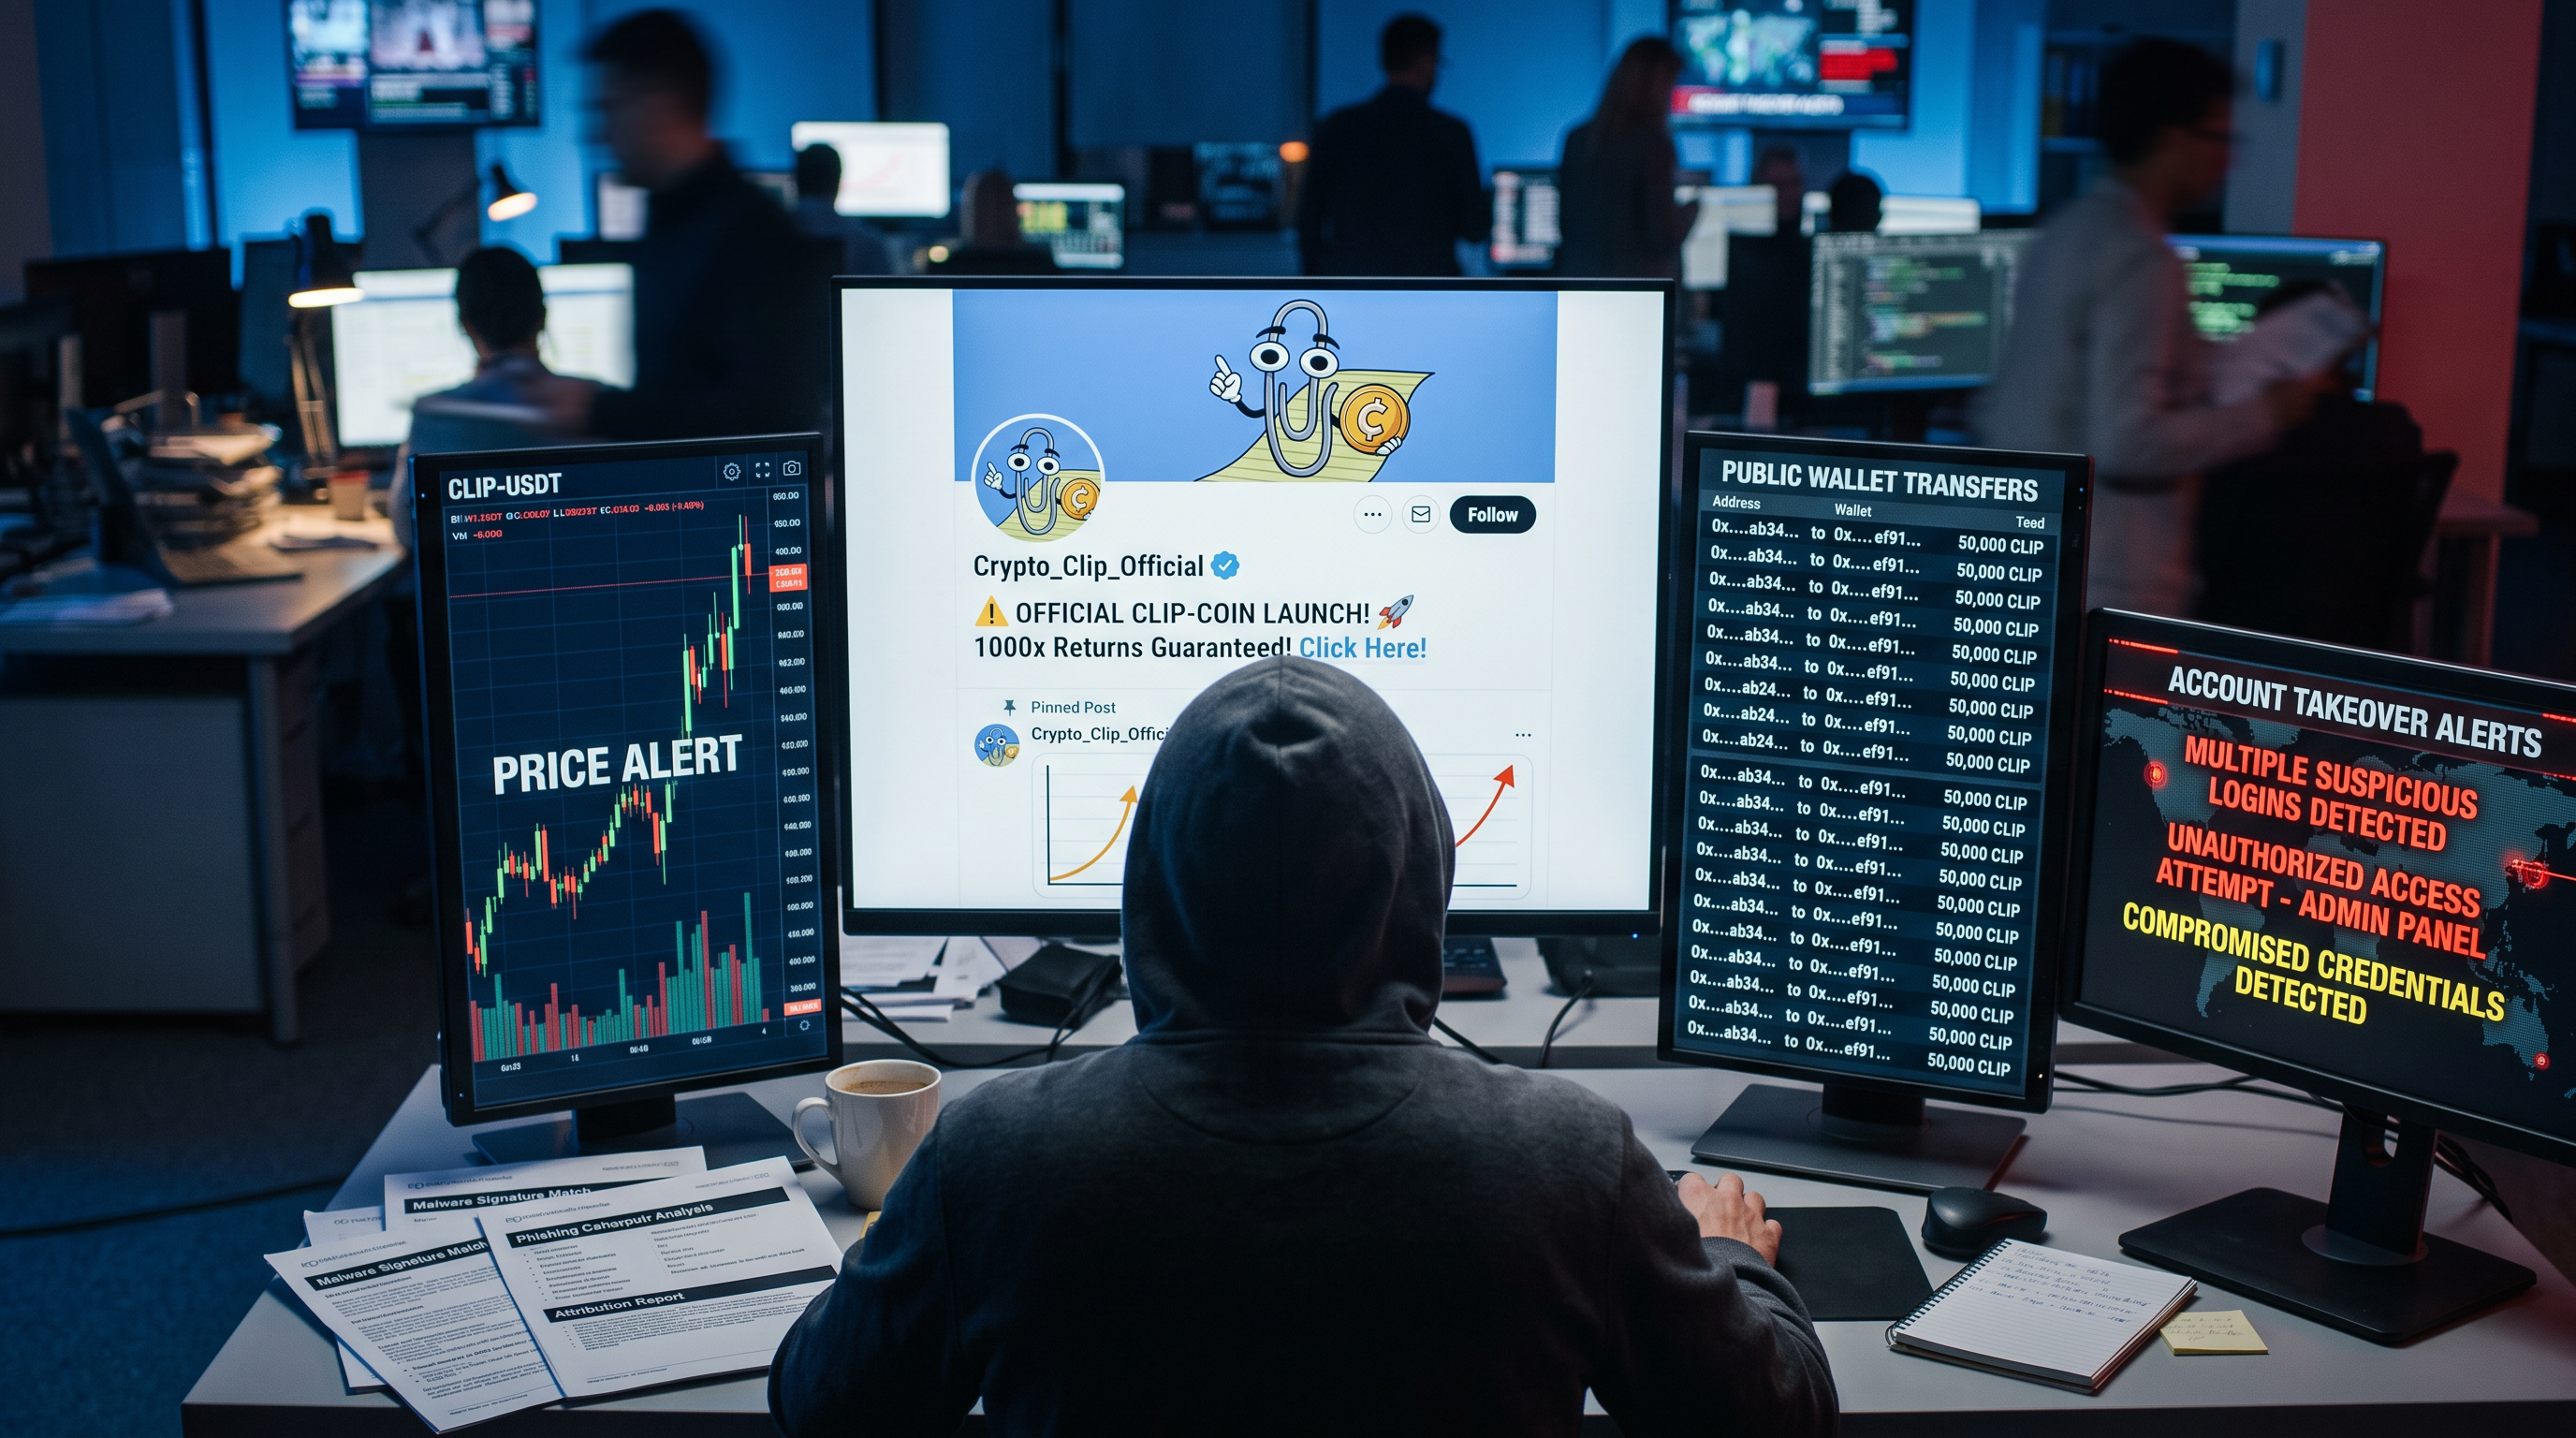
One of the biggest brand names in technology just became a billboard for a meme coin. Hackers took over the official Microsoft account on X, which has more than 13 million followers, and used it to boost a Clippy-themed cryptocurrency token. The Microsoft X account hacked story is a sharp reminder that a verified badge and a famous logo do not make a financial pitch trustworthy.
Key facts
- Attackers compromised the official @Microsoft account on X, which has more than 13 million followers, according to security reporting published in early October 2026.
- The hijacked account was used to amplify posts and accounts promoting an unauthorized token called $CLIPPY, which is not an official Microsoft product.
- Microsoft confirmed unauthorized access, said it had secured the account, and removed the unauthorized posts, according to the reports.
- Security outlets characterized the campaign as an attempted cryptocurrency pump-and-dump, and no verified public loss figure has been reported.
What happened when the Microsoft X account was hacked
The incident was first reported around October 2, 2026, and drew follow-up coverage in the days afterward. According to BleepingComputer, the attackers used the company's main X profile to promote a crypto token tied to Clippy, the animated paperclip assistant that many longtime Office users remember.
The posts and amplified accounts pushed the $CLIPPY token. Because they appeared on a verified corporate account, the pitch looked like it carried an endorsement from Microsoft. It did not. The token has no connection to the company.
Reports from SecurityWeek, The Verge, and TechRadar describe the same core event: a hijacked brand account, a nostalgic mascot, and a speculative token.
Microsoft's response to the unauthorized access
Microsoft confirmed that someone had gained unauthorized access to the account. The company said it had secured the account and removed the unauthorized posts.
It is important to be clear about roles here. Microsoft was the target of the compromise. It is not accused of taking part in the token promotion, and nothing in the cited reporting suggests it benefited from it.
The reports do not say publicly how the attackers got in. Until the company or investigators share more detail, the method of compromise remains unconfirmed.
How the $CLIPPY pump-and-dump scheme works
Security reporting described the campaign as an attempted pump-and-dump. That label matters, so it helps to understand what it means and what it does not prove.
The basic pump-and-dump playbook
A pump-and-dump relies on manufactured attention. Promoters create buzz around a low-profile asset, buyers rush in, and the price rises. Those who hold large amounts of the asset can then sell into that demand, often leaving late buyers with tokens that fall sharply in value.
Meme coins are a common vehicle because anyone can create one cheaply, and their value often depends almost entirely on hype. A borrowed brand name is the fastest way to generate that hype.
Why a hijacked brand account is so effective
Most people judge a post by who appears to have said it. When a message comes from an account with 13 million followers and a verification mark, many readers lower their guard. Attackers know this and aim to borrow that trust for a few hours, which can be long enough to attract buyers.
The Clippy angle added a second hook. Nostalgia makes a post feel playful and harmless, which can make a risky financial pitch feel less like a pitch at all.
Was any money lost in the Microsoft X hack?
No verified public loss figure appears in the cited reporting. That gap is worth stating plainly. Calling the campaign a pump-and-dump describes the alleged intent and structure. It does not prove that a specific amount was stolen or that any particular buyer lost money.
Readers should treat any dollar figure circulating on social media with caution unless it comes from a named, credible source. If investigators or blockchain analysts publish verified numbers later, the picture could change.
Why the Microsoft X account hacked incident matters
This was not a fake account pretending to be Microsoft. It was the real account. That distinction undermines a piece of advice many people rely on, which is to check that the profile is authentic before trusting a post.
Authenticity of the account is no longer enough. A real account can be seized, and a real badge can sit on top of a fraudulent message. Several things follow from that:
- Large brand accounts are high-value targets because their audiences are huge and trusting.
- Verification confirms identity at a point in time, not the safety of every post that follows.
- Any unsolicited investment offer, even from a familiar name, deserves independent checking.
Impersonation tied to famous names is a recurring pattern. Our coverage of MrBeast impersonation giveaway scams and Taylor Swift deepfake giveaway scams shows how scammers keep borrowing recognizable faces and brands to move people toward risky offers.
How to spot a fake crypto promotion
You do not need technical skills to avoid most of these traps. A short checklist covers the most common red flags.
- Look for urgency. Phrases such as "buy now" or "limited window" are designed to stop you from thinking.
- Check the company's own channels. If a major company launched a token, its website, press page, and investor relations pages would say so. Silence there is a warning.
- Be wary of unknown tokens. A brand-new token with no track record, no audit, and no clear team is high risk even without a scam.
- Ignore the follower count. Reach says nothing about legitimacy, especially if an account may have been compromised.
- Never connect your wallet to a link from a social post. Many fake promotions also include wallet-draining sites.
Crypto fraud also has real legal consequences for those who run it. For one example of how courts treat these cases, see our report on Adam Iza's sentence in a crypto fraud case.
What brands and account owners can do
The incident also carries lessons for companies and creators who manage large social profiles. Basic account security reduces the odds of a takeover and limits the damage if one happens.
- Use phishing-resistant multi-factor authentication, such as hardware security keys, on every admin login.
- Limit how many people and third-party apps can post from the main account.
- Keep a rapid response plan so unauthorized posts can be removed and followers warned quickly.
- Pin a clear notice when something goes wrong, so followers know which messages to ignore.
Where to report crypto scams and account hijacking
If you saw the posts and bought the token, or you suspect you were targeted by a similar promotion, report it. In the United States, you can file a report with the FTC at reportfraud.ftc.gov or with the FBI Internet Crime Complaint Center at ic3.gov.
Keep screenshots, wallet addresses, transaction IDs, and links. Those details help investigators trace funds and connect separate complaints. Also report the posts to the platform so they can be reviewed.
The bottom line
The Microsoft X account hacked incident shows how quickly trust can be turned into a sales tool. A real account with 13 million followers briefly lent its credibility to a token that Microsoft did not create or endorse. Microsoft says it has secured the account and removed the posts, and no verified loss figure has been published.
The practical lesson is simple. Treat every investment pitch as unverified until you confirm it somewhere independent, no matter whose name is attached. Share this article with anyone who follows crypto trends, and report suspicious promotions the moment you see them.
Frequently Asked Questions
Was the Microsoft X account really hacked?
Yes. According to security reporting from early October 2026, Microsoft confirmed unauthorized access to its official @Microsoft account on X. The company said it secured the account and removed the unauthorized posts.
Is the $CLIPPY token an official Microsoft product?
No. The $CLIPPY token is not a Microsoft product, and Microsoft was the target of the account compromise, not a participant in the promotion. Anyone who sees the token linked to Microsoft should treat that claim as false.
How much money did people lose in the Microsoft crypto scam?
No verified public loss figure has been reported. Security outlets described the campaign as an attempted pump-and-dump, but that description does not prove a specific amount was stolen.
What is a crypto pump-and-dump scheme?
A pump-and-dump is a scheme where promoters hype an asset to drive up demand and price, then sell their holdings to those late buyers. The price often drops afterward, leaving later buyers with losses. Meme coins are a common target because their value depends heavily on attention.
How can I tell if a crypto promotion from a big brand is real?
Check the company's official website, press releases, and investor pages for confirmation, rather than relying on a single social post. A verified account can be hijacked, so authenticity of the profile does not prove the message is genuine. If the offer is urgent or involves an unknown token, treat it as a red flag.