Imagine hiring a cybersecurity firm specifically because you do not want to pay the criminals who just locked your files. Now imagine that firm allegedly paid those criminals anyway, with your money, and told you nothing. That is the core of the MonsterCloud ransomware fraud case announced by federal prosecutors on October 8, 2026.
Key facts
- Federal prosecutors charged Zohar Pinhasi, owner of Florida ransomware-recovery company MonsterCloud, on October 8, 2026, over an alleged scheme targeting businesses already hit by cyberattacks.
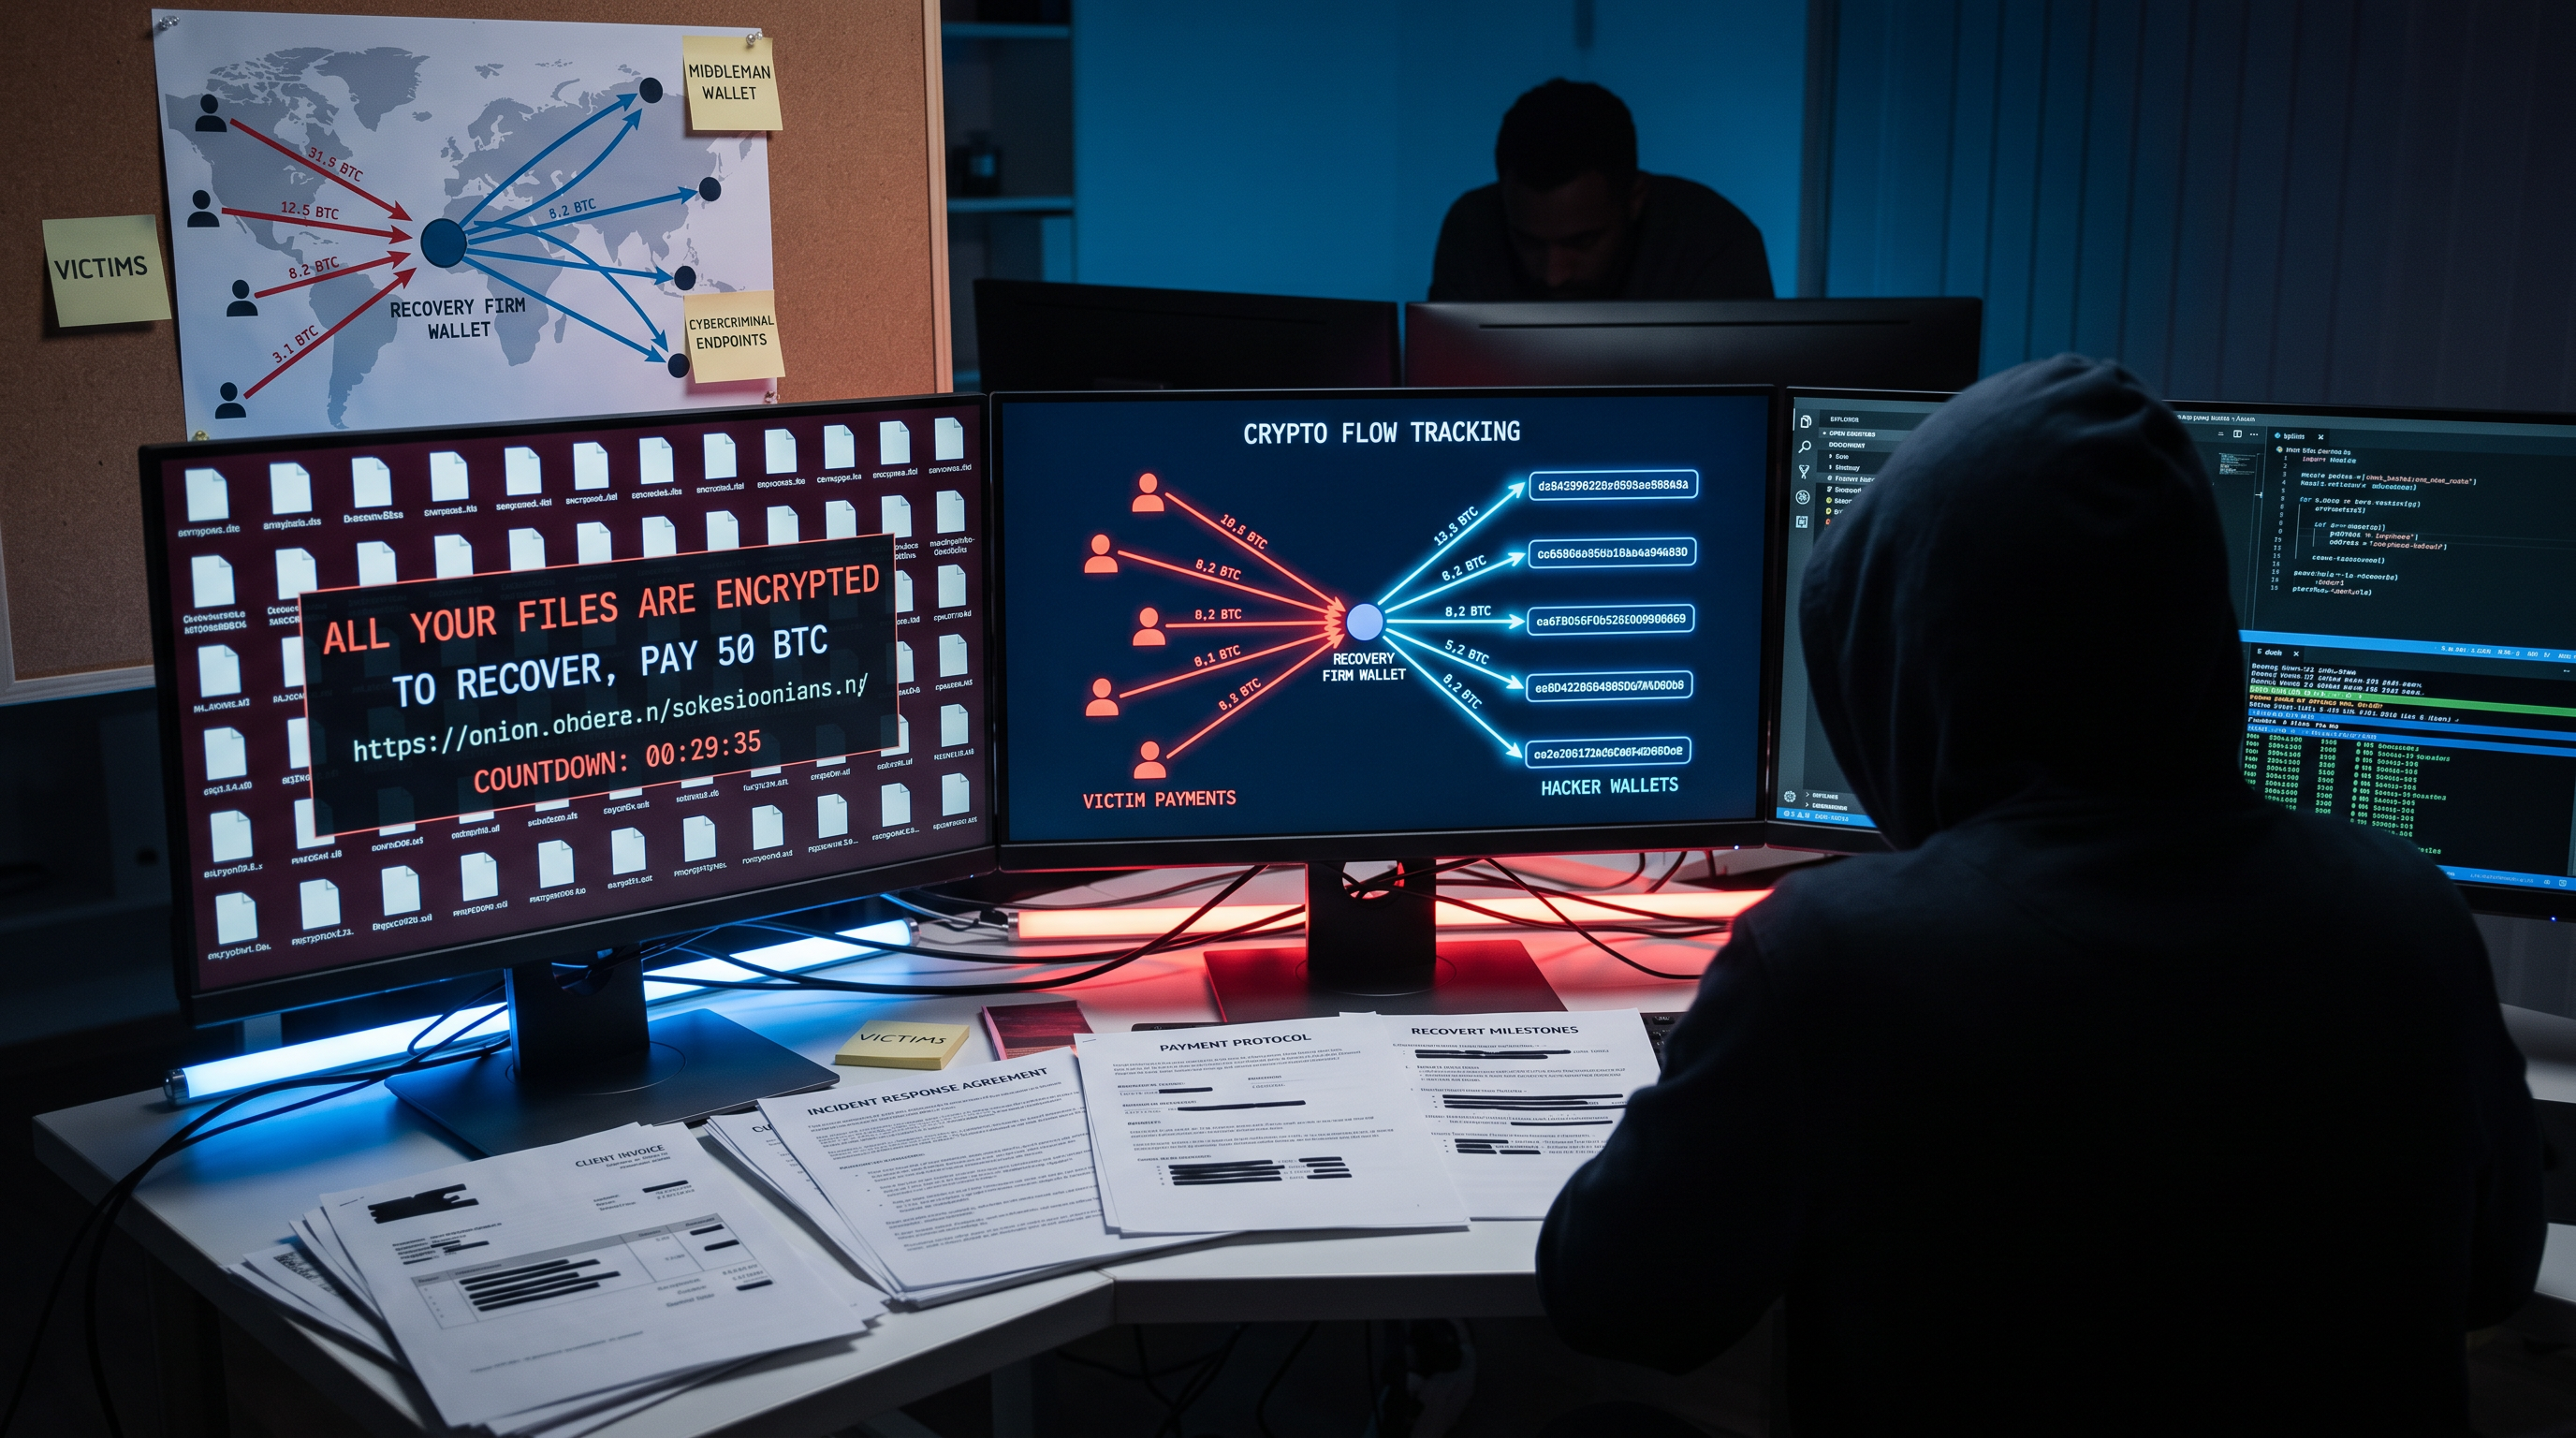
- According to prosecutors, Pinhasi told clients MonsterCloud could recover ransomware-encrypted files without paying the attackers, while he allegedly negotiated with the criminals and paid them for decryption tools.
- Reporting based on the charges says MonsterCloud billed clients more than $19 million and paid more than $8 million to ransomware operators.
- Pinhasi faces federal wire-fraud-related charges, has not been convicted, and the allegations remain unproven.
What prosecutors allege in the MonsterCloud ransomware fraud case
According to the Justice Department, Pinhasi runs MonsterCloud, a Florida company that marketed itself as a ransomware remediation and recovery provider. He is also known as Zack Silver and Zack Green, according to the charging reports. The Justice Department announcement describes him as a known cybersecurity expert.
A separate release from the U.S. Attorney's Office, posted on the Eastern District of New York site, frames the case as one of defrauding clients. Everything described below is an allegation. No court has found Pinhasi guilty.
The promise made to ransomware victims
Ransomware victims are often in a panic. Systems are locked, operations are stalled, and a countdown clock may be ticking on a ransom note. Many organizations want to avoid paying attackers, both because payment funds more crime and because there is no guarantee the criminals will deliver working keys.
Prosecutors allege MonsterCloud pitched itself to exactly these businesses. The claim, according to the charges, was that the company could recover encrypted files without paying the attackers.
The alleged hidden payments to hackers
Prosecutors say the reality was different. They allege that behind the scenes, Pinhasi negotiated with the ransomware criminals and paid them for decryption tools. He then allegedly concealed those payments from the customers who had hired his company to avoid that very outcome.
The Hacker News report on the case, along with coverage from The Record, centers on this reversal. The company that promised to beat the hackers allegedly paid them instead.
The numbers: billings versus ransom payments
Two figures stand out in the coverage. Reporting based on the charges says MonsterCloud billed clients more than $19 million. It also says the company paid more than $8 million to ransomware operators.
Those numbers need careful reading. They describe billings and alleged ransom payments. They are not a court-established theft total, and they do not prove how much any victim lost. A judge or jury would have to decide what the evidence shows, and loss calculations typically get argued in detail if a case reaches trial or sentencing.
- More than $19 million: amount reportedly billed to clients.
- More than $8 million: amount reportedly paid to ransomware operators.
- Not established: a final fraud or loss figure.
Who is Zohar Pinhasi?
Pinhasi is the owner of MonsterCloud, which is based in Florida. Reports say he has also used the names Zack Silver and Zack Green. The Justice Department's description of him as a known cybersecurity expert suggests he had a public profile in the industry, which is part of why the allegations drew attention from outlets such as Help Net Security.
He faces federal wire-fraud-related charges. Wire fraud generally covers schemes to obtain money through false statements carried out using electronic communications. As with any criminal case, he is presumed innocent unless and until he is convicted or pleads guilty.
Why this ransomware recovery fraud case matters
Ransomware recovery is a trust-heavy business. Victims rarely have the technical skill to check what a vendor is doing, and they are under heavy time pressure. That imbalance can make any hidden practice hard to spot.
If the allegations hold up in court, the case would show how a provider could turn that imbalance into profit. The alleged harm goes beyond money. Customers were reportedly told one thing about how their data would be restored, while a different and undisclosed process was allegedly used.
Wire fraud prosecutions involving deception about how money is used are not rare. For a comparison from another case, see our report on the Kerr Kriisa wire fraud guilty plea. For a different type of alleged investor deception, read about the Adam Iza crypto fraud sentence.
What the case does not show
It is important to stay precise here. The case does not suggest that every ransomware recovery or incident response firm works this way. Many legitimate firms disclose when a ransom negotiation or payment is part of the plan, and some clients choose that route knowingly.
Nor do the reports say MonsterCloud itself deployed ransomware. The allegation is about how the company dealt with attackers who had already hit its clients, and what it told those clients.
How to vet a ransomware recovery company
No checklist removes all risk, but a few questions can expose red flags before you sign a contract. Ask them in writing and keep the answers.
- Ask how recovery will work. Request a plain description of the method, including whether any contact with the attackers is expected.
- Ask about ransom payments. Get a written statement of whether the firm will ever negotiate or pay, and require your approval first.
- Request itemized billing. Third-party costs, including any payments to outside parties, should be visible on invoices.
- Check independent references. Speak with past clients and look for regulatory or court records.
- Involve your lawyer and insurer. Counsel and cyber insurance carriers often have vetted vendor lists and legal obligations around ransom payments.
- Contact law enforcement. Report the attack early, because agencies may have decryption resources or intelligence.
Where to report ransomware recovery scams
If you believe a recovery provider misled you, preserve contracts, emails, invoices, and chat logs. Then file a report with the FTC at ReportFraud or the FBI Internet Crime Complaint Center. Ransomware attacks themselves can also be reported to the FBI through IC3.
What happens next
Pinhasi's case now moves through the federal court process. That typically includes an initial appearance, pretrial motions, and possible plea negotiations or a trial. Prosecutors carry the burden of proving the charges beyond a reasonable doubt.
Further filings may clarify how the billing and payment figures were calculated, which clients were affected, and how the alleged payments were hidden. Until then, the $19 million and $8 million figures remain reported allegations tied to the charges.
Conclusion: trust, but verify your recovery vendor
The MonsterCloud ransomware fraud case, if proven, would be a sharp example of a rescue service allegedly working against the people it promised to help. For now, it is an unproven set of federal allegations against Zohar Pinhasi, who has not been convicted.
The practical lesson holds either way. Before you hire anyone to handle a ransomware incident, demand clear answers about methods, payments, and billing. If something feels off, report it to the FTC or the FBI, and follow our coverage at Blacklist for updates on this case and other alleged frauds.
Frequently Asked Questions
Who is Zohar Pinhasi?
Zohar Pinhasi is the owner of MonsterCloud, a Florida ransomware-recovery company. He is also known as Zack Silver and Zack Green, according to reports on the charges. Federal prosecutors charged him on October 8, 2026, and he has not been convicted.
What is MonsterCloud accused of doing?
Prosecutors allege MonsterCloud told clients it could recover ransomware-encrypted files without paying the attackers. They say the company instead negotiated with the criminals, paid them for decryption tools, and hid those payments from customers. The allegations are unproven.
How much money is involved in the MonsterCloud case?
Reporting based on the charges says MonsterCloud billed clients more than $19 million and paid more than $8 million to ransomware operators. These figures describe billings and alleged ransom payments. They are not a court-established theft total.
Do all ransomware recovery companies pay hackers?
No, and the case does not suggest that. Many legitimate firms are open with clients about whether any negotiation or payment is part of the response, and clients decide with full information. The allegation here concerns concealment from customers.
Where can I report a ransomware recovery scam?
You can file a report with the FTC at reportfraud.ftc.gov or with the FBI Internet Crime Complaint Center at ic3.gov. Keep contracts, invoices, emails, and messages as evidence. Contact your lawyer and cyber insurer as well.